The AI Agent Scale Problem Is Arriving Quickly
Enterprise AI used to summarize documents, propose next steps and help people find information faster, while a person made the final decision.
Agents now finish the work themselves. They plan a task, use the tools available to them and see it through. Work that passed through several hands can move from start to finish in one flow with no one in between.
The numbers are moving fast. Gartner predicts that by 2028 the average global Fortune 500 enterprise will have more than 150,000 agents in use, up from fewer than 15 in 2025. They will come from different teams and platforms: agents running core business processes alongside shortcuts an employee built to save a few hours a week. Without a clear view of what exists, leaders have no basis for deciding how much responsibility any one agent should carry.
Confidence is Running Ahead of Control
In a September 2026 survey of 362 US IT decision-makers by Guild.ai and Morning Consult, 96.4% said they were confident their agent inventory was complete and accurate. Only 39.8% kept logs or audit trails for their agents, and only 31% could stop a malfunctioning agent with an automated kill switch. Two-thirds had dealt with an agent-related operational incident in the previous 12 months.
An agent can pass every test in a pilot and still raise hard questions once it is live. Someone has to own it. Its access has to be defined. The business needs to know how fast it can step in when the agent does something unexpected. When those answers are missing, the move from pilot to production stalls.
“Agents that work well in a demo still have to earn their place in the business.”
AI Agent Autonomy Should Be Earned in Four Levels
Agents scale best when their freedom matches their track record. Gartner defines four levels of autonomy: observe, advise, act with approval, and act autonomously within guardrails. Each level sets what the agent can do, how much a person stays involved and which controls have to be in place.
|
Autonomy level
|
What the agent can do
|
Human involvement
|
Controls that have to be in place
|
|
1. Observe
|
Reads approved information, retrieves data and summarizes findings.
|
A person reviews the output and decides what to do.
|
Read-only access, authentication, a defined data scope and activity logging.
|
|
2. Advise
|
Analyzes information, finds patterns and recommends actions.
|
A person evaluates and approves the recommendation before anything runs.
|
Data restrictions, output validation, visible sources and a review workflow.
|
|
3. Act with approval
|
Prepares or starts actions in connected systems.
|
A person authorizes consequential actions before they execute.
|
Role-based permissions, approval checkpoints, action logs and rollback where the system supports it.
|
|
4. Act autonomously within guardrails
|
Executes approved tasks on its own within set limits.
|
A person supervises exceptions, performance and risk.
|
Strict permissions, runtime monitoring, policy enforcement, cost alerts and a way to stop the agent.
|
A supplier invoice agent shows how an agent moves through them. It starts by flagging invoices that do not match purchase orders. Once its accuracy is proven, it recommends which ones to approve. Next it processes routine invoices below a set value after someone signs off. Eventually it handles standard invoices on its own, while people review the exceptions and the audit log instead of every decision.
The risk is in governing every agent the same way. Gartner warns that uniform governance leads to agent failure, and predicts that by 2027, 40% of enterprises will demote or decommission autonomous agents because of governance gaps found only after a production incident. Matching controls to each level lets an organization extend autonomy with its boundaries in plain sight.
Autonomy is also not a permanent grant. When an agent's purpose, data access, tools, model or operating environment changes, its level should be reassessed.
Three questions every agent has to answer
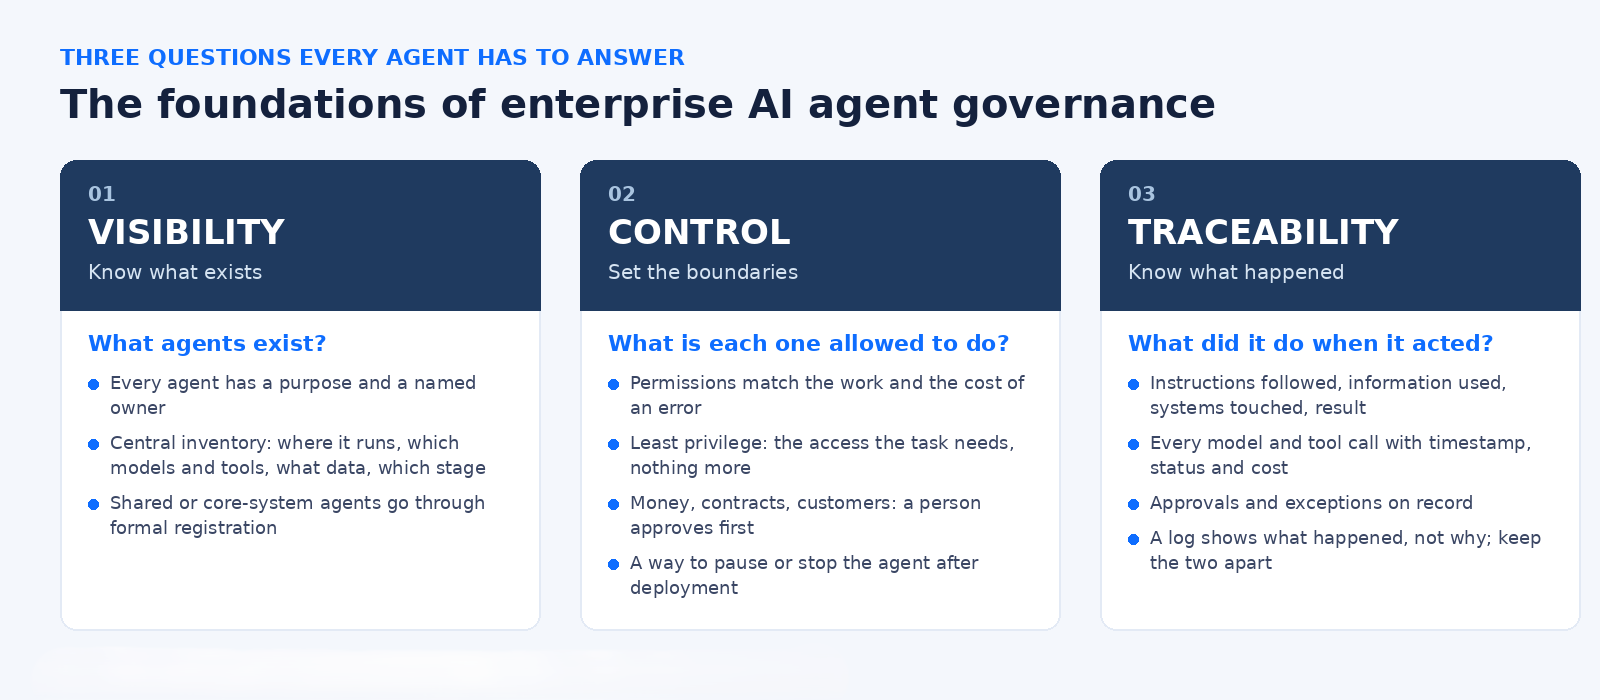
Performance alone does not earn an agent more autonomy. Before scaling, the business needs answers to three questions. What agents exist? What is each one allowed to do? What did it do when it acted? The answers rest on visibility, control and traceability.
Visibility: know what exists
Every agent has a stated purpose and a named owner. A central inventory records where it runs, which models and tools it uses, what data it can reach and whether it is in development, testing or production. Agents shared across teams or wired into core systems go through formal registration and review. Only 35.9% of organizations in the Guild.ai survey require registration before an agent goes live.
Control: decide what agents can do
Permissions match the work and the cost of an error. The agent's role, the data involved and the impact of a mistake decide when it acts alone and when it needs approval. Least privilege applies: an agent gets the access its task needs and nothing more. Actions involving money, contracts or customers keep a person in the loop before they complete. Control continues after deployment, which means runtime policy enforcement and a way for an authorized team to pause or stop an agent.
Traceability: show what happened
Every decision shows the instructions the agent followed, the information it used, the systems it touched and the result, with a way to reverse that result when needed. Useful records include the agent and session identifiers, each model and tool call with its timestamp and status, actions taken in connected systems, approvals and exceptions, and token usage with its cost.
One distinction matters here. An activity log shows what an agent did. It does not by itself explain why the agent reached a conclusion. Treat the two separately.
“When every decision can be traced, trust stops being a guess and becomes something the businesses can prove.”
That evidence pays off beyond compliance. When the information needed to review an agent is already on hand, approvals move faster. Teams spend their time deciding what the agent can take on next instead of reconstructing what happened.
What changes when AI agents reach production
Once agents are live, occasional reviews are no longer enough. Agents act within seconds, so rules on sensitive data, privacy and compliance have to apply every time an agent runs. When a rule is breached, the response has to be immediate: block the action, escalate it or pause the agent.
Five things need an owner before the first production agent goes live.
Ownership. A named person is responsible for the agent's purpose, permissions, performance and periodic review, with technical ownership and business accountability both defined.
Access. The agent reaches approved data and systems only. Personal data is handled under the privacy policy the organization already has.
Testing and promotion. The agent is evaluated before production and evaluated again when its configuration, tools, models or permissions change. A controlled promotion path keeps untested changes out of business-critical environments.
Monitoring and intervention. Teams can see what the agent is doing and can stop it when its actions carry operational risk.
Cost. Agents consume far more compute than earlier AI tools, and spend rises fast when every task runs on the most capable model. Track cost by agent and model, decide which agents may use which models and set alert thresholds early. That also shows leaders which agents deliver enough value to earn more responsibility.
The operating model matters too. Responsibility for AI today is split among IT, dedicated AI teams and business functions. Scaling agents means agreeing who sets the rules, who watches agents in production and who decides when an agent moves up or down a level. If you want one record of what an agent did and what it cost, start with agent observability and control.
Regulation is raising the bar
Accountability is becoming a formal requirement. The EU AI Act requires high-risk AI systems to log events automatically over their lifetime (Article 12) and to be designed for human oversight, including the ability to interrupt the system (Article 14).
Those obligations do not apply to every agent. They depend on the system's intended purpose and classification, so an enterprise should assess each agent rather than treat all of them as high-risk. The operational lesson applies either way: know how the system works, keep oversight in place and keep records that support accountability.
For banking, healthcare and other regulated industries, the controls that let agents scale are the same controls that support compliance. Putting them in place early means the question of control does not get reopened each time an agent takes on more. A management system standard such as ISO/IEC 42001 gives that work a frame, and the industry specifics are covered in our guide for CIOs in BFSI, healthcare and manufacturing.
How SERAA Cortex answers the three questions
SERAA Cortex is Covasant's operating system for the enterprise agent lifecycle. It is generally available, and Covasant is ISO/IEC 42001 certified. Four modules carry an agent from first build to live production, and three of them can be adopted on their own, which matters when most of an estate was built somewhere else.
Agent Registry: what exists2
Agent Registry is the universal catalogue. It discovers and catalogues the agents you run on Gemini Enterprise, Azure AI Foundry, AWS Bedrock and Databricks Agent Bricks alongside the ones SERAA Cortex deploys, so the inventory the survey respondents were confident about exists in one place. Each agent moves through Dev, QA, Staging and Production with version lineage, and semantic versioning shows a diff before publish. Deployment to GKE, AKS, EKS, Cloud Run, Azure Functions, Google Agent Engine or Azure AI Foundry runs from one workflow, and any agent SERAA Cortex deployed can be undeployed from the same place.
Agent Control Tower: what it can do, and what it did
Agent Control Tower sets guardrail policies per tenant and per agent: content filters, PII detection and redaction, and GDPR and HIPAA policies, applied through the model gateway whatever the underlying model. Scope-based access control works at system, organization and project level, so an agent operates at the autonomy its owners have set. Every LLM call lands in a searchable log with timestamp, status, session ID, agent, model, tokens and per-call cost. Cost is attributed by agent, model, user, provider and tenant, with budget alerts at the thresholds you set.
Agent Work Bench and orchestration: building to the standard
Agent Work Bench supports no-code and pro-code agents in one interface, with a Playground for model-by-model validation before deployment. Agent Test Bench, now in beta, generates scenario and persona-based tests from the agent's knowledge base and an interview with your subject-matter experts, runs them and scores answer relevancy, hallucination, bias, toxicity and role adherence across runs. Multi-Agent Orchestration adds human-in-the-loop steps inside a workflow, which is how “act with approval” gets enforced rather than hoped for.
One boundary is worth stating. Agent Control Tower observes the agents SERAA Cortex deploys. Runtime observability for agents running on the external platforms above is on the roadmap. Today, Agent Registry catalogues them and Agent Control Tower governs what runs through SERAA Cortex.
A global welding and cutting manufacturer runs four finance agents on SERAA Cortex in its global shared services and has cut claims cycle time by more than seven days. Across engagements, Covasant reports LLM cost reductions of 40 to 60% from governed model routing.*
Autonomy scales when accountability scales with it
As agents take on more of the work, the organizations that tie autonomy to accountability will have the most room to extend what those agents are trusted to do. The ones that cannot answer the three questions will be the ones writing decommission tickets in 2027.
Autonomy scales when accountability scales with it.
See the agents already running in your enterprise in one registry, with controls at the level each one has earned.
Book a SERAA Cortex demo