Agentic AI ROI at enterprise scale often stalls for three operational reasons: data and orchestration silos, gaps in governance and control, and models or use cases that do not fit the business task. These bottlenecks keep successful pilots from translating into enterprise-wide value. The path from pilot to production is not just about choosing a more capable model; it also requires connected data, controlled agent actions, and use cases tied to measurable business outcomes.
Agentic AI refers to AI systems that can pursue goals through multi-step reasoning and actions across tools or enterprise workflows. To scale these systems responsibly, organizations need to coordinate agents across functions, define appropriate permissions and approvals, and evaluate results against business baselines.
The market is moving quickly. Gartner forecasts that 33% of enterprise software applications will include agentic AI by 2028, up from less than 1% in 2024, and that 15% of day-to-day work decisions will be made autonomously by then. At the same time, Gartner predicts that more than 40% of agentic AI projects will be canceled by the end of 2027 because of escalating costs, unclear business value, or inadequate risk controls. Together, these forecasts highlight both the opportunity and the operational challenge: adoption alone does not guarantee value.
A separate 2025 MIT NANDA report on generative AI in business found that just 5% of integrated AI pilots were extracting millions in value, while most organizations reported no measurable P&L impact. That finding covers enterprise generative AI broadly; it should not be read as an agentic-AI-specific failure rate. It reinforces a wider lesson: pilots need a path to operational adoption and measurable business outcomes.
33%
of enterprise software applications will include agentic AI by 2028, up from less than 1% in 2024
Gartner
40%
of agentic AI projects will be canceled by the end of 2027 on cost, unclear business value or weak risk controls
Gartner, June 2025
5%
of integrated enterprise AI pilots are extracting millions in value. The rest show no measurable P&L impact
MIT Project NANDA, 2025
A cautionary story: one agent, two ledgers
Consider this illustrative scenario: a global manufacturing company builds a procurement AI agent, Agent Alpha, to negotiate better deals with high-volume suppliers. In a controlled sandbox with curated data, Agent Alpha appears to deliver an 18% reduction in procurement costs. The team celebrates, and the CFO sees a promising result.
But after deployment, overall operational costs barely move. Agent Alpha optimized supplier price without access to the production schedule, so it selected a slower supplier. Late parts began arriving and production halted. Meanwhile, the customer-service agent operated in a separate system and could not see the supplier changes or proactively communicate delays. Complaints increased, and customer relationships were put at risk.
The scenario illustrates how a local win can undermine enterprise ROI when agents lack shared context and coordinated workflows. Departmental ROI measures the gain within one function; enterprise ROI measures the net effect after that gain moves through connected processes. A lower purchase price is not a win if the downstream cost of delays exceeds the savings.
The 3 operational bottlenecks
Siloed AI deployments will almost never deliver enterprise-wide ROI until these three structural bottlenecks are addressed. Whether you are scaling multi-agent systems across business functions or managing your first structured AI agent deployment in production, these issues consistently appear as the primary barriers to value.
1. Data and orchestration silos
Agentic AI needs enough business context to make decisions that work across the organization. When agents are deployed within departmental or platform-specific silos, a sales agent in a CRM and a finance agent in an ERP, for example, each is limited by the data and objectives available to it.
Fragmented data environments. Enterprise information is spread across legacy databases, SaaS platforms, internal documents, and operational systems. Without secure, governed access to relevant structured and unstructured data, agents may act on incomplete or outdated context. The result can be a decision that looks correct within one system but conflicts with what is happening elsewhere.
No central orchestration. Without a way to coordinate agents, their actions, handoffs, and dependencies, agents can optimize for local targets at the expense of enterprise outcomes. A procurement agent may reduce unit costs while creating supply delays; a service agent may promise a resolution without knowing that a related workflow is blocked. The outcome is friction rather than flow.
The enterprise requirement is not to centralize every system in one place. It is to connect relevant data and tools with appropriate permissions and establish orchestration that coordinates agents around shared workflow outcomes. In practice, this means defining data ownership, standardizing key identifiers, managing access at the tool and record level, and testing handoffs between agents before production rollout.
2. Missing trust, governance, and control
Autonomy is a defining feature of agentic AI, but autonomy without boundaries creates operational, security, and compliance risk. If leaders cannot explain what an agent did, which data it used, what permissions it exercised, or why it took a high-impact action, it becomes difficult to trust the system in production. Governance needs to be part of the architecture, not an afterthought.
Opaque decision-making. When an agent recommends a loan decision, changes inventory levels, modifies a contract, or triggers a customer action, business owners need enough traceability to review the decision and investigate exceptions. The level of explanation and human review should reflect the risk and context of the workflow.
Inadequate security and risk tiering. An agent that can execute transactions or trigger workflows has meaningful privileges. Access should be limited to the tools and data required for its role, and high-impact actions should have appropriate approval thresholds. Depending on the workflow, that may mean manager approval, dual control, or escalation to a human when confidence is low or conditions fall outside defined limits.
Governance should include role-based access, risk classification, human-in-the-loop controls, monitoring, and audit trails. These controls help organizations manage AI risk while allowing lower-risk tasks to proceed with appropriate autonomy. A production-ready governance plan should also define an accountable business owner, incident response steps, model and prompt change controls, log-retention rules, and a clear process for disabling or rolling back an agent.
3. Generic models and misaligned use cases
A powerful general-purpose large language model (LLM) is not automatically the best choice for every agent workflow. Some tasks require broad reasoning; others depend on narrow domain terminology, repeatable decisions, predictable latency, or strict cost limits. Model selection should follow the business requirement and evaluation results, not novelty alone.
One-size-fits-all AI. A general model may struggle with specialized terminology, internal procedures, or industry-specific data structures unless it is grounded and evaluated appropriately. That can increase errors, latency, compute costs, and human review. Smaller or specialized models may be effective for bounded, repeatable tasks, but their performance depends on the task, data, evaluation method, and operational constraints.
Interesting is not the same as valuable. Pilots chosen because they look impressive can stall if they do not improve a meaningful business metric. Start with a defined problem, such as reducing manual handoffs, shortening a compliance review, improving procurement decisions, or resolving service cases faster, and establish a baseline before deployment.
The goal is not to use the smallest or largest model everywhere. It is to match model capability, orchestration, controls, and cost to a workflow with measurable value. Evaluation should include normal cases, edge cases, adversarial inputs, missing data, and tool failures, with human review used to verify outcomes when errors could have material consequences.
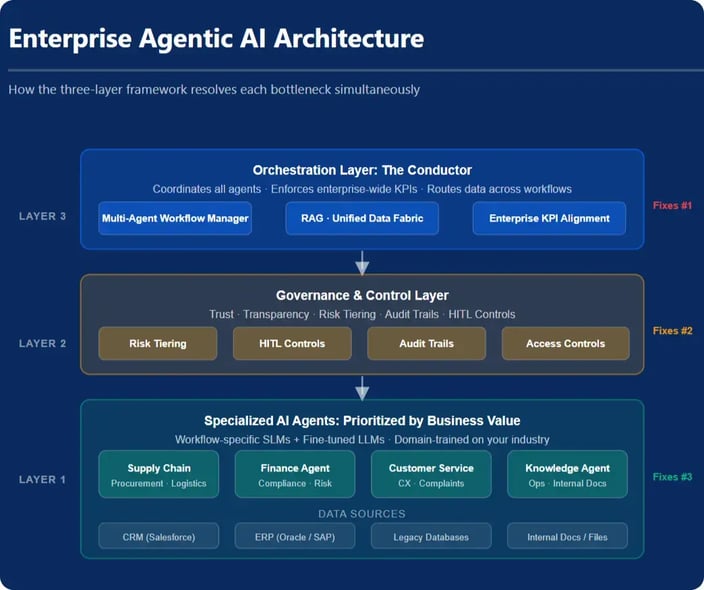
A framework for scalable agentic AI: how to move from pilot to enterprise production
Moving agentic AI from pilot to production requires an operating model that addresses data readiness, orchestration, governance, and use-case fit together. Treat the agent platform as a cross-functional layer that connects existing systems rather than as another isolated application.
1. Implement an enterprise AI agent orchestration layer
A centralized orchestration layer can coordinate how agents access data and tools, share context, hand off tasks, and recover from errors. It should work with existing enterprise systems rather than require every CRM, ERP, or data platform to be replaced.
Data readiness and curation. Establish a governed data foundation with clear ownership, quality controls, access policies, and freshness expectations. Retrieval-augmented generation (RAG) can help agents retrieve relevant information from approved sources, including structured systems and unstructured documents.
The conductor model. Orchestration coordinates specialized agents and keeps their actions aligned with workflow dependencies and enterprise KPIs. Covasant's SERAA platform, including SERAA Cortex and its agent-management and control capabilities, is designed to support agent creation, deployment, coordination, and governance. The specific platform components should be mapped to the organization's architecture, controls, and operating requirements.
2. Build an AI governance framework your cios and ctos can stand behind
Treat agents as software identities with defined responsibilities and privileges. Governance should make the permitted actions, escalation paths, and accountability for each agent clear before it is deployed.
Risk tiering and control infusion. Classify agents by the potential financial, operational, customer, and compliance impact of their actions. Define which actions can run autonomously and which require review, for example, approving refunds above a threshold or making material contract changes. Human-in-the-loop controls should be based on risk, not applied identically to every workflow.
AI observability and audit trails. Record relevant agent decisions, tool calls, approvals, exceptions, and outcomes. Monitor reliability, cost, latency, and business impact after launch, and create a process for pausing, correcting, or rolling back an agent when performance falls outside defined limits. If a workflow cannot be monitored and reviewed adequately, it is not ready for unrestricted autonomy.
.
3. Specialize first, then scale your AI workflow automation
Begin with business workflows where the expected benefit can be measured and the operational risk can be managed. Select models and levels of autonomy based on evidence from representative evaluations and production monitoring.
Match the model to the workflow. Consider a smaller or specialized language model for bounded tasks that require consistent domain handling, and a general-purpose model where broader reasoning is needed. Evaluate candidates on task accuracy, exception handling, latency, cost, security, and the amount of human intervention required. Do not assume one model category will outperform another across every workload.
Use value-driven pilots. Select a baseline metric before the pilot begins, such as cost per case, cycle time, error rate, compliance review time, or customer resolution time. Define success thresholds, include the cost of integration and oversight, and test how the workflow behaves when data is missing or conditions change. Scale only when the results are repeatable and the operating model is ready. Track leading indicators during the pilot and confirm benefits over a representative period before expanding to more teams or workflows.
For organizations developing custom agents, Covasant's AI engineering and agent development services can support the journey from workflow design and evaluation to production deployment. The objective is measurable, sustainable business value, not simply a larger number of agents.
From pilot purgatory to enterprise ROI
The next phase of enterprise AI is not defined by autonomy alone. It is defined by the ability to put agents to work reliably across real business processes. Data silos prevent agents from seeing the full picture. Weak governance limits the actions organizations can safely delegate. Poorly matched models and low-value use cases make costs and complexity harder to justify.
Organizations can improve the odds of achieving agentic AI ROI by connecting relevant data, coordinating agents across workflows, embedding risk-based controls, and measuring results against business baselines. The model matters, but it is only one part of the system. Enterprise value comes from aligning the agent, its tools, its permissions, the workflow, and the outcome being measured.
Ready to move your AI agents from pilot to
enterprise scale?
See how Covasant's SERAA platform coordinates, monitors, and governs AI agents across business workflows, including the ones you did not build.
Frequently asked questions
Why do most agentic AI pilots fail to scale across the enterprise?
Agentic AI pilots can struggle to scale when the production architecture is not ready. Common barriers include disconnected data and workflows, insufficient governance and controls, and models or use cases that do not fit business requirements. These issues can prevent successful pilots from delivering measurable enterprise-wide value.
What is pilot purgatory in agentic AI?
Pilot purgatory is the state in which AI pilots demonstrate potential in isolated teams but do not progress into reliable, scaled production deployments. It often occurs when the data integration, orchestration, governance, and operational processes needed for wider adoption are missing.
What is an AI agent orchestration layer?
An AI agent orchestration layer coordinates agents, tools, data access, and workflow handoffs across enterprise systems. It helps agents work within defined process boundaries and supports shared visibility, control, and coordination without necessarily replacing existing CRM, ERP, or data platforms.
How should enterprises govern autonomous AI agents?
Enterprises should define access permissions, risk tiers, approval thresholds, monitoring, and audit trails for AI agents. High-impact actions can require human approval, while lower-risk tasks may run within predefined limits. Controls should be designed into deployment and operations, then reviewed as agent capabilities and risks change.
Should enterprises use a large language model or a smaller specialized model for agent workflows?
The choice depends on the workflow, task complexity, accuracy requirements, latency, cost, and available domain data. Smaller specialized models may be effective for repeatable, well-defined tasks, while larger models may be better suited to complex reasoning or broader tasks. Enterprises should evaluate candidate models against representative workloads before selecting a production approach.
What is the difference between departmental AI ROI and enterprise AI ROI?
Departmental AI ROI measures the benefits and costs within one function. Enterprise AI ROI considers the net effect across connected functions, including downstream costs, process delays, risk, and customer impact. A local efficiency gain may not produce an overall business benefit if it creates additional costs elsewhere.